We are worrying about AI while the foundations fail
Nov 10, 2026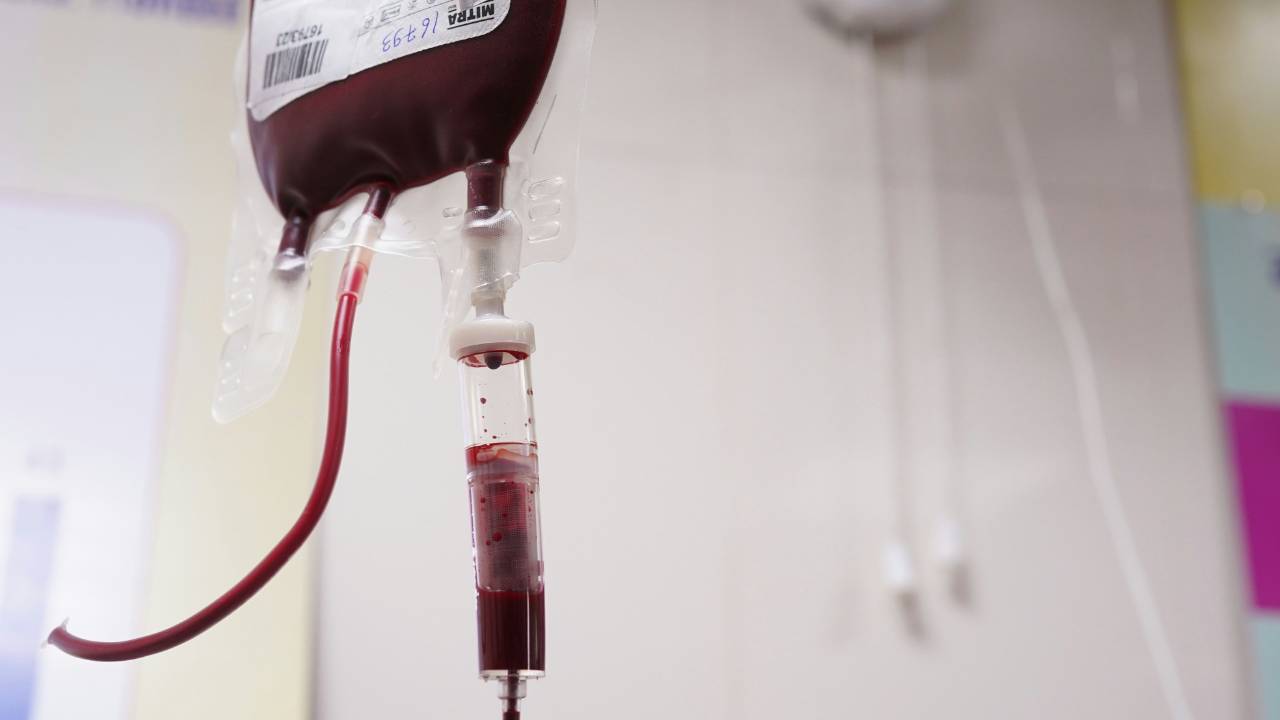
How much intelligence does it take to turn off a fridge?
Rather less than it takes to build a frontier AI model. Yet interfering with refrigeration can destroy food, threaten medical supplies and interrupt services on which thousands of people depend. We should think rather harder about that when deciding which technological threats deserve our attention.
Stephen Bush’s recent FT commentary, drawing on an observation by former National Cyber Security Centre chief Ciaran Martin, raises an uncomfortable question about our priorities. Stories about AI models bypassing safeguards generate enormous interest. Attacks on the infrastructure supporting everyday life struggle to command the same sustained attention.
I think we have the balance wrong.
AI poses serious questions about employment, accountability and security. But while we argue about its future capabilities and whether development should slow down, existing technology already allows attackers to disrupt businesses and essential services. They do not need to wait for the next breakthrough.
A fridge can become a healthcare risk
On 2 November, a cyber incident involving a refrigeration supplier affected three sites operated by the French Blood Establishment. Temperature settings were altered. Alarms and prompt action by staff prevented blood products or samples from being compromised.
The fact that the response worked is reassuring. The exposure is rather less so.
The blood service did not have to be attacked directly for its operations to be threatened. A supplier’s systems provided the route through which disruption reached an essential service. How many leadership teams understand their own dependencies well enough to recognise a similar exposure?
The incident also demonstrates the value of people who know what to do. Monitoring detected the problem, staff responded and supplies were protected. Resilience becomes real when someone can act effectively under pressure.
Have we made efficiency too fragile?
Supermarkets make the economic dilemma particularly clear. Accurate forecasting, automated stock management and closely timed deliveries reduce waste and help keep prices competitive. Each improvement makes commercial sense.
But those improvements also increase dependence on the systems coordinating the operation. If refrigeration fails, stock becomes unsaleable. If ordering and distribution systems fail, food can be available in one place while shelves remain empty somewhere else.
In October, attacks on refrigeration systems in French supermarkets forced stores to discard food after temperatures rose. A digital intrusion had an immediate physical consequence.
The leadership question is how much room the business retains to recover. Are there alternative ways of working? Do staff know how to use them? How long can the operation tolerate disruption before customers, suppliers and cash flow are seriously affected?
A process can be highly efficient under normal conditions and extremely difficult to operate when those conditions change. If the business case measures only normal performance, the board is approving an incomplete picture.
Having run technology businesses, I know that reliability costs money. Spare capacity, alternative suppliers, maintenance and rehearsed recovery arrangements all need funding. Their value is hardest to demonstrate on the days when everything works. That makes them easy targets when leaders are looking for savings.
The saving appears immediately. The exposure can remain invisible until something fails.
The digital economy has physical foundations
We speak about digital services as though they exist somewhere beyond the physical world. They depend on electricity, buildings, cooling equipment and cables. Their apparent convenience can conceal a complicated chain of dependencies.
The European Commission’s Joint Research Centre reports that subsea cables carry as much as 99 per cent of internet traffic between continents. Most cable damage is accidental, although some incidents have raised concerns about deliberate interference. Repair capacity and the time needed to restore connections are significant constraints.
An accident and an attack have different causes. They can expose the same weakness.
Nor should we assume that every successful cyber attack requires extraordinary technical sophistication. The NCSC’s 2026 review says that most successful compromises still rely on familiar methods, including known vulnerabilities, stolen credentials and social engineering.
That should make leaders uncomfortable. We cannot explain away every failure as the work of an adversary whose capabilities were impossible to anticipate.
What does the board actually know?
I would ask a leadership team to describe what happens when a critical system or supplier becomes unavailable. Which customer commitments fail first? How quickly does that happen? What can staff still do safely? Who has the authority to change priorities?
Then I would ask for evidence.
When was recovery last rehearsed under realistic conditions? Did it work within the time the business could tolerate? If two suppliers provide an alternative, do they depend on the same underlying infrastructure?
These questions concern operations, cash, customer trust and leadership behaviour. Technical specialists must inform the answers. Executives must own the decisions, including the cost of reducing exposure and the consequences of accepting it.
Governments have a corresponding responsibility for essential services and shared infrastructure that no individual business can protect alone.
We should examine AI risks carefully. But slowing AI development would not repair the weaknesses in the systems we already depend on. Those require attention, investment and decisions now.
If a critical system failed tomorrow, could your business keep operating? When did you last test that?